Find the cryptography a quantum computer will break.
Morrow finds the RSA and elliptic-curve cryptography across your estate, ranks it by what it protects, and tracks every fix through to post-quantum algorithms.
- Category
- PQC governance
- Standards
- FIPS 203 · 204 · 205
- Output
- CycloneDX 1.6 CBOM
- License
- MIT
Harvest now, decrypt later.
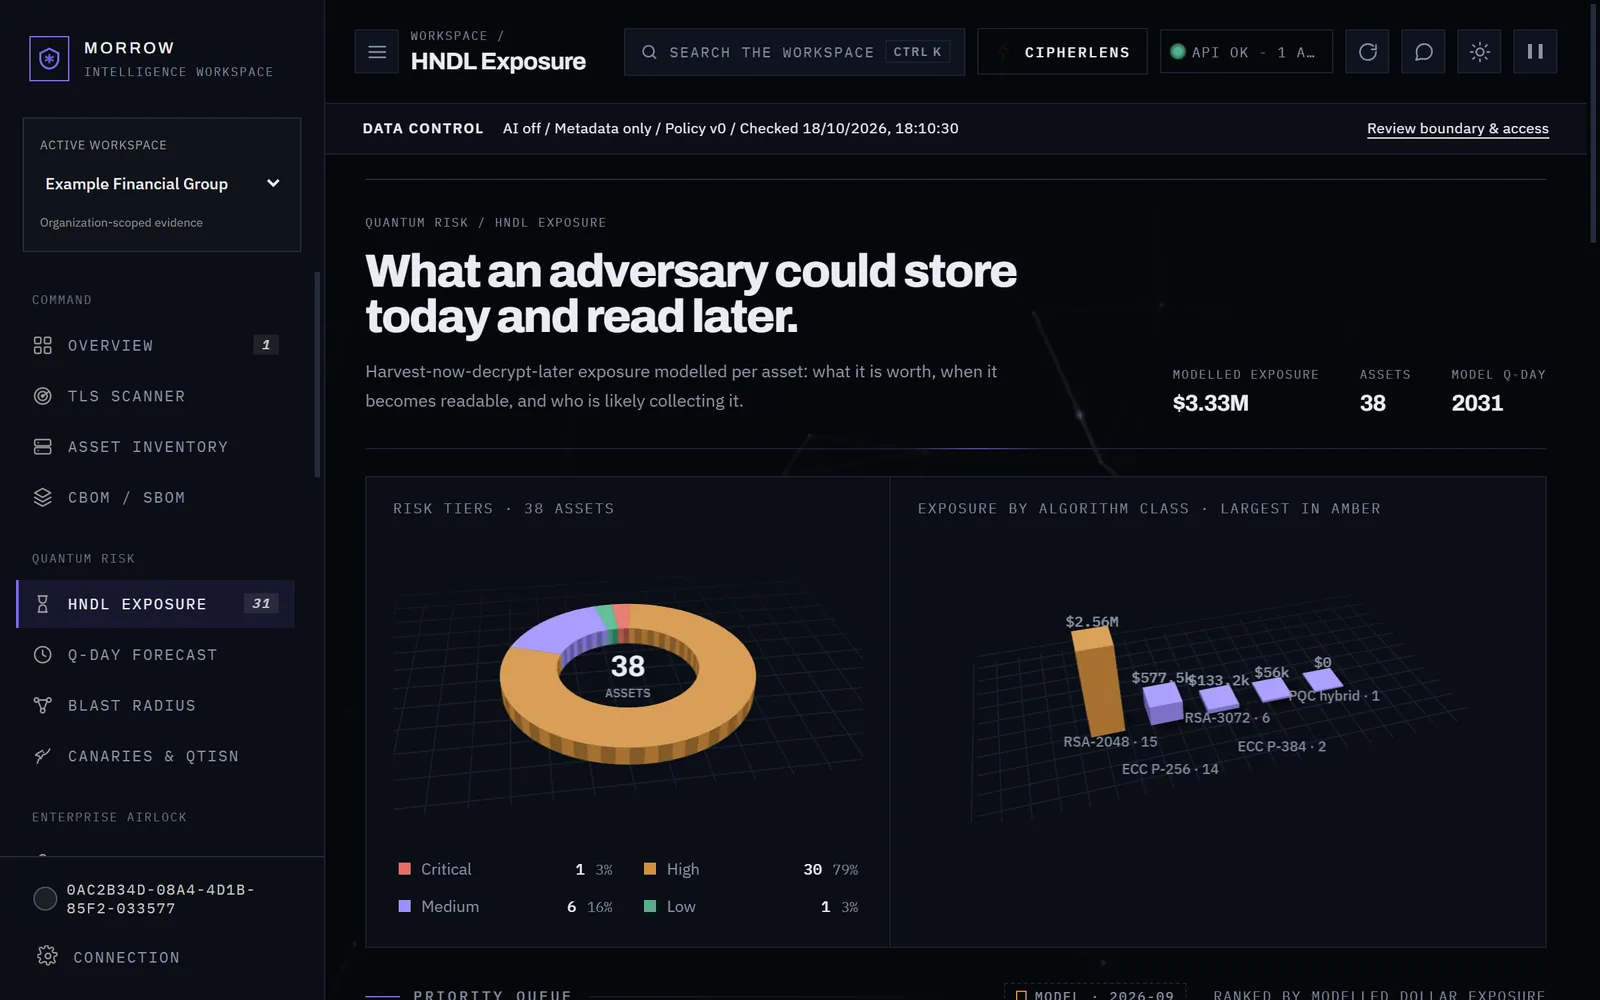
Nobody has built a quantum computer that breaks RSA yet. That does not make it a future problem: traffic recorded today can be stored and decrypted on the day one exists. Anything that must stay secret for a decade is exposed the moment it crosses a network protected only by classical public-key cryptography.
Milestones from NIST IR 8547. The Q-day band is a range of published estimates, not a prediction.
Is your data already exposed?
If the years your data must stay secret plus the years your migration takes exceed the years until a quantum computer arrives, you are already late. Morrow works this out for every asset; try it for one.
Data you send today could be read 5 years before it stops mattering. The migration has to start before the quantum computer exists.
From inventory to proof.
Migration is an inventory problem first. You cannot replace cryptography you cannot find, and you cannot prove it is gone without a record of who fixed what.
- 01
Discover
Probes TLS endpoints for the key exchange, signature and key size actually negotiated, including hybrid groups such as X25519MLKEM768. Scans source and cloud configuration for crypto primitives and key material.
- 02
Score
Ranks every finding by algorithm, key size and how long the data behind it must stay secret, so a ten-year customer record outranks a test server.
- 03
Assign
Each asset carries an owner, team, environment and criticality. A finding becomes someone's task, not a line in a report.
- 04
Remediate
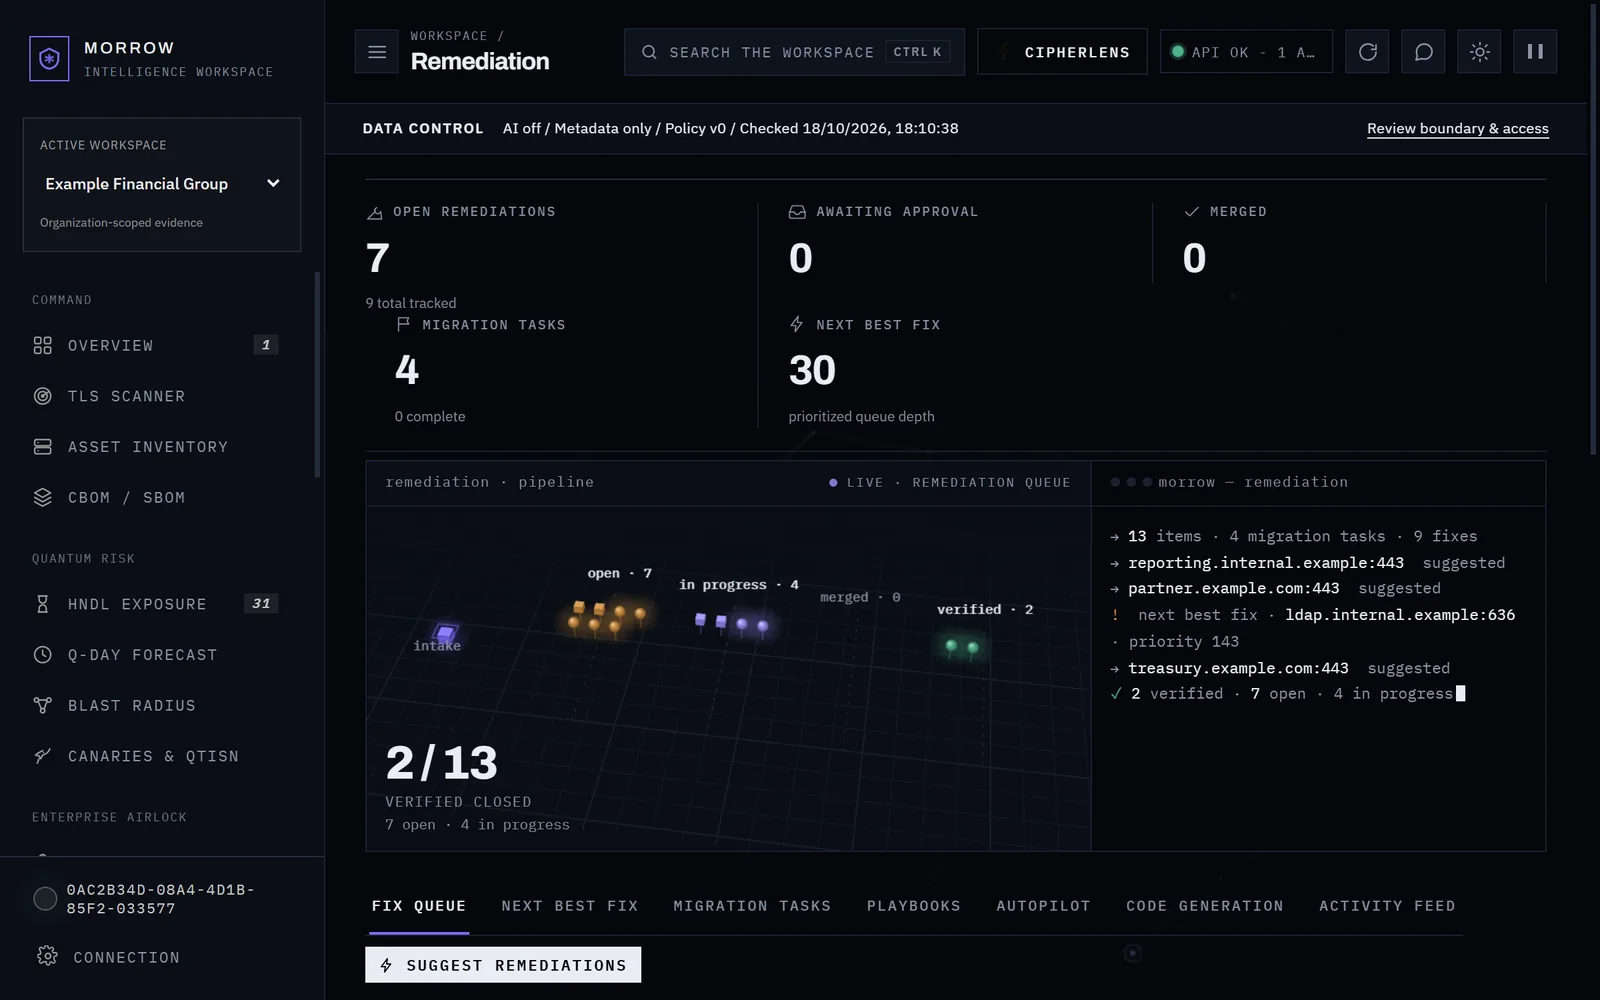
Suggested, approved, pull request, merged. Fix plans name the exact file to change, and drift checks reopen anything that regresses.
- 05
Prove
Signed remediation bundles, compliance reports, an append-only audit journal and a CycloneDX 1.6 CBOM for auditors.
Built for the people who sign off.
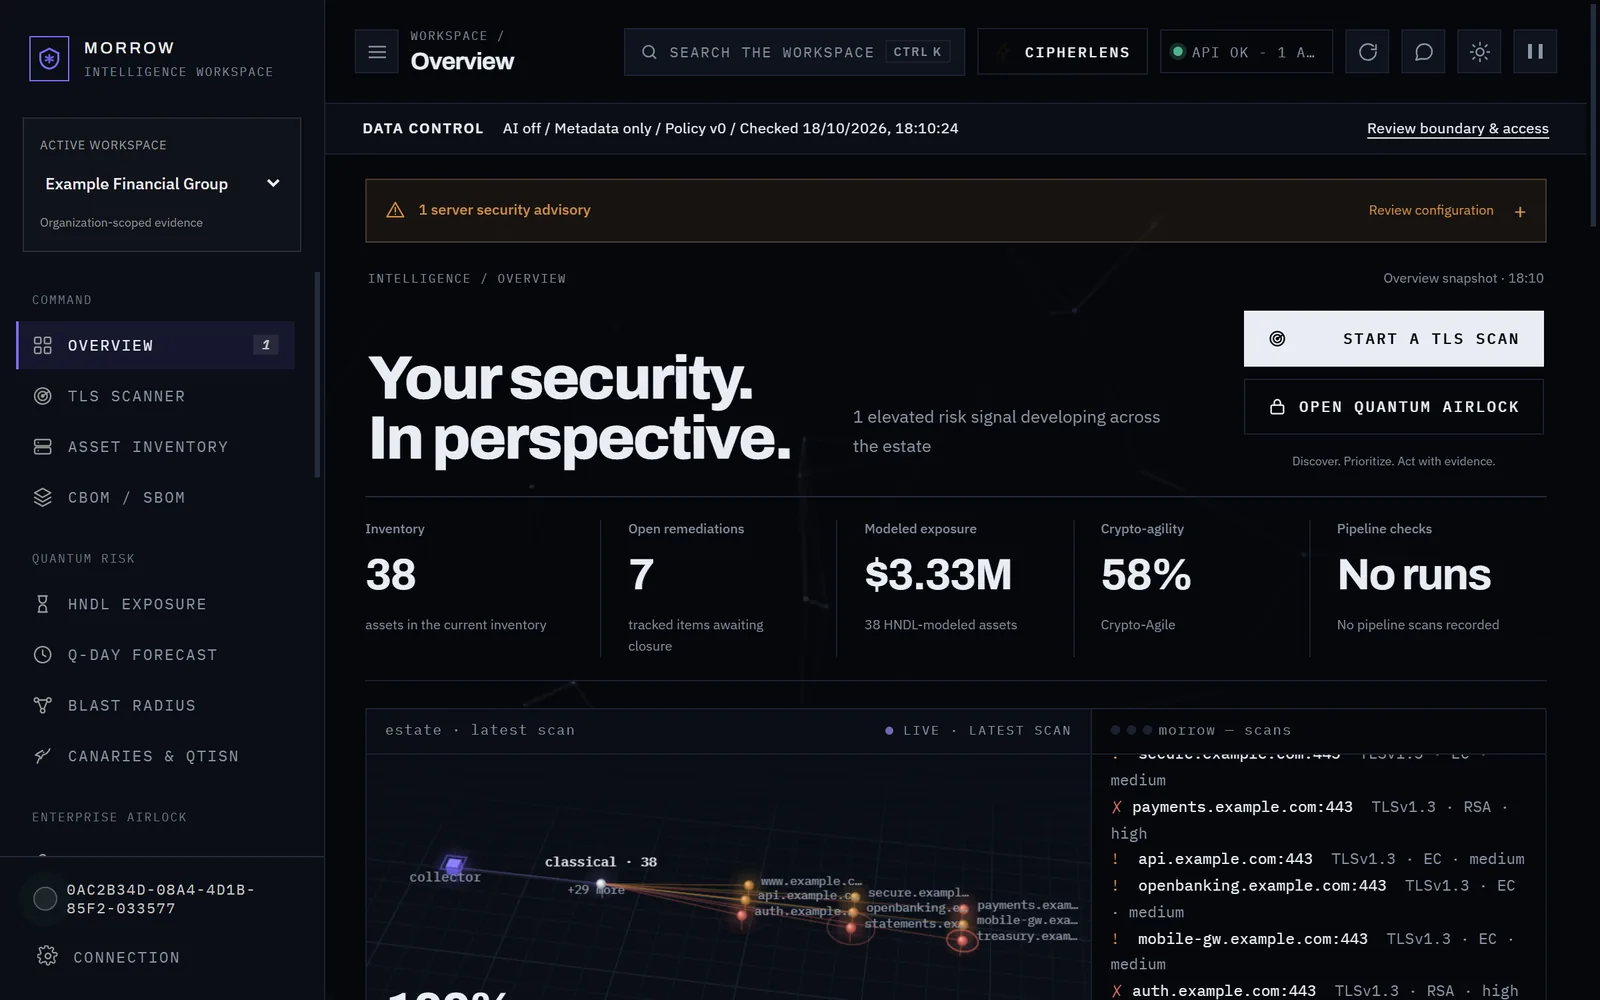
Morrow is a post-quantum cryptography governance platform. It discovers the cryptography in use across TLS endpoints, certificates, source repositories and cloud configuration, scores what is exposed, assigns every finding an owner, and tracks it through remediation to verified closure.
Discovery
Probes endpoints and certificates for key exchange and signature algorithms, and scans code and cloud configuration.
Quantum risk scoring
Ranks findings by algorithm, key size and how long the protected data must stay confidential.
Ownership
Every asset carries an owner, team, environment and criticality, so nothing is left unassigned.
Remediation workflow
Suggested, approved, PR created, verified closed, with drift checks after the fix.
CBOM export
A CycloneDX 1.6 Cryptography Bill of Materials for auditors and supply-chain tooling.
Evidence
Signed remediation bundles, compliance reports and an append-only audit journal.
- FIPS 203
- ML-KEM key encapsulation
- FIPS 204
- ML-DSA signatures
- FIPS 205
- SLH-DSA hash-based signatures
- NIST IR 8547
- Transition timeline to 2035
- CycloneDX 1.6
- Cryptography Bill of Materials
Run it on your own servers.
Your scan results describe your weakest systems, so they should not leave your network. One command starts the whole platform with Docker; no database to install and no account to create.
$ git clone https://github.com/soqlab/morrow
$ cd morrow
$ docker compose up --build

# optional: a fictional bank to explore
$ docker compose run --rm seed

✓ console at http://localhost:8001/ui/